- Overview
- Verified and unverified vulnerabilities
- Filter or search vulnerabilities
- Ignore an unverified vulnerability
- Remove a vulnerability from the ignored list
- CVE, CVE IDs, and CVSS
Overview
The Vulnerabilities module in UpGuard Breach Risk lists vulnerabilities identified from information exposed in HTTP headers, website content, and open ports. As UpGuard scans from outside companies' networks, it can confirm some vulnerabilities (verified vulnerabilities), but others it only knows may exist, based on the software version detected (unverified vulnerabilities).
The MITRE ATT&CK column, and the MITRE ATT&CK techniques section in a vulnerability's details, show the attacker techniques each vulnerability is mapped to. Select a technique in that section to see a description of it and which of your other findings are mapped to it. For more, see Breach Risk: MITRE ATT&CK Techniques.
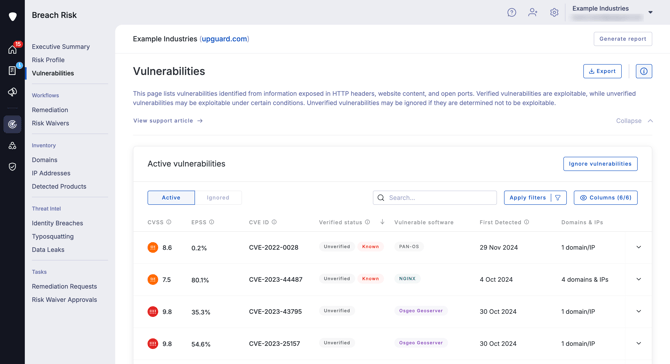
Verified and unverified vulnerabilities
Unverified vulnerabilities may be exploitable. When UpGuard finds one of your websites running a specific software version with known vulnerabilities, it often can't verify whether the vulnerability exists. It can only verify that the vulnerability may exist, based on the exposed information. A patch that doesn't change the detectable software version could also mitigate it. This is why unverified vulnerabilities appear as informational risks in other parts of UpGuard, such as your Risk Profile or risk remediation workflows.
Verified vulnerabilities are exploitable and have risk classifications. For some vulnerabilities, UpGuard can run a specific test that confirms the domain is vulnerable. The details of each test are unique to each Common Vulnerabilities and Exposures (CVE) entry. When verified vulnerabilities are detected, you'll see them in your Risk Profile. You can use them in remediation and risk waiver workflows, as you can with other risks.
The known label means a vulnerability is on CISA's list of known exploited vulnerabilities. Investigate any unverified vulnerability with this label to find out whether the affected systems are likely to be exploited.
Filter or search vulnerabilities
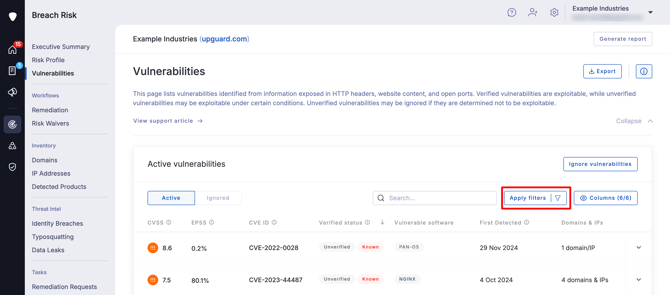
- In Vulnerabilities, select Apply filters. A panel slides out from the right side of your screen.
- Choose your filters. You can filter by label, verified status, CVE ID, software, CVSS severity, EPSS score, and MITRE ATT&CK technique. The MITRE ATT&CK techniques filter has its own section, below Label.
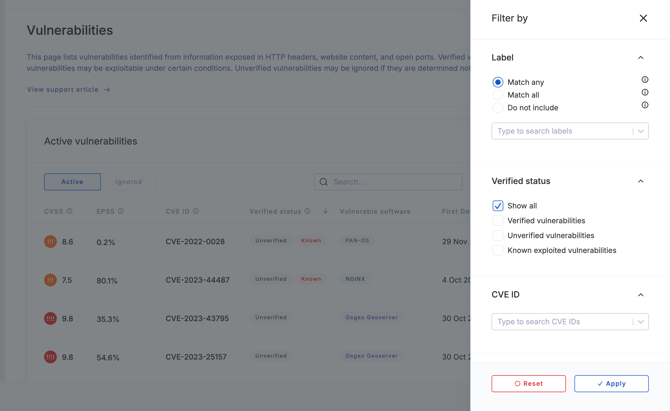
- Select Apply.
To find a specific vulnerability, select the search box and search by its CVE ID.

Ignore an unverified vulnerability
You can ignore an unverified vulnerability once you've confirmed it doesn't apply to a system — for example, it's been patched but the software version hasn't been upgraded yet. Ignoring it removes it from the displayed list.
Ignoring a vulnerability is different from a risk waiver. When you ignore a vulnerability, you're signaling that the risk doesn't exist. With a risk waiver, you're accepting the risk.
- Select Ignore vulnerabilities in the upper right-hand corner of the vulnerabilities table. Your screen changes so you can select vulnerabilities.
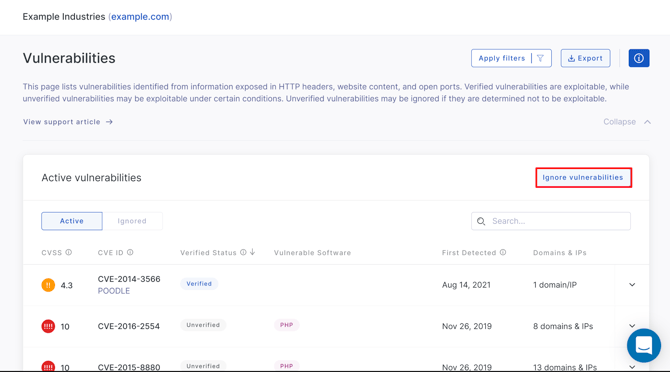
- Select the checkbox to the left of the CVSS column for each vulnerability you want to ignore.
- Select Ignore vulnerabilities.
The vulnerabilities are removed from the displayed list.
Remove a vulnerability from the ignored list
- In Vulnerabilities, select the Ignored tab.
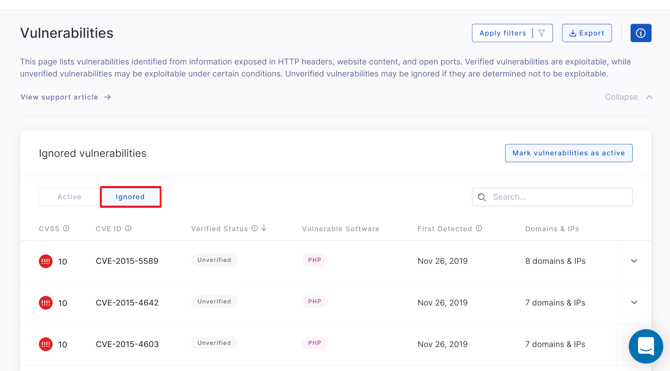
- Select Mark vulnerabilities as active. Your screen changes so you can select vulnerabilities.
- Select the checkbox to the left of the CVSS column for each vulnerability you want to mark as active.
- Select Mark vulnerabilities as active.
The vulnerabilities are removed from the ignored list and marked as active.
If you want to find a specific vulnerability, select the search box and search by its CVE ID.
CVE, CVE IDs, and CVSS
Common Vulnerabilities and Exposures (CVE) is a database of publicly disclosed vulnerabilities. The vulnerabilities reported in Breach Risk's Vulnerabilities section have been published to it. Each vulnerability in CVE is described as a known vulnerability or exposure, with a brief description and references to related vulnerability reports and advisories. Unlike vulnerability databases, CVE entries don't include risk, impact, fix, or other technical information.
The MITRE corporation launched CVE in 1999 to identify and categorize vulnerabilities in software and firmware. MITRE is a nonprofit that operates federally funded research and development centers in the United States.
A CVE ID is the standard identifier, with a status indicator, that each vulnerability in CVE is given. It's formatted as CVE-YYYY-NNNNN, where YYYY is the year the CVE ID was assigned or the year the vulnerability was made public — for example, CVE-1999-0067, CVE-2014-12345, or CVE-2016-7654321. UpGuard shows each vulnerability's CVE ID.
Common Vulnerability Scoring System (CVSS) is a published standard that captures a vulnerability's main characteristics. It produces a numerical score between 0 and 10 that reflects severity. UpGuard uses CVSS v3 where it's available, and CVSS v2 for vulnerabilities that predate v3.